По данным OpenNet, в PHP найдена уязвимость — удалённое выполнение кода (CVE-2026-115560). Точные затронутые версии не указаны. Версия с исправлением в сообщении не указана.
Что сделать сейчас: Проверьте, вышло ли обновление PHP с исправлением, и установите его.
ADOdb is a PHP database class library that provides abstractions for performing queries and managing databases. In versions 5.22.9 and below, improper escaping of a query parameter may allow an attacker to execute arbitrary SQL statements when the code using ADOdb connects to a sqlite3 database and calls the metaColumns(), metaForeignKeys() or metaIndexes() methods with a crafted table name. This is fixed in version 5.22.10. To workaround this issue, only pass controlled data to metaColumns(), metaForeignKeys() and metaIndexes() method's $table parameter.
Средний · CVSS 6.1EPSS 0,9%Публичный эксплойтНет опубликованного исправления
CVE-2025-51502
Reflected Cross-Site Scripting (XSS) in Microweber CMS 2.0 via the layout parameter on the /admin/page/create page allows arbitrary JavaScript execution in the context of authenticated admin users.
Средний · CVSS 6.1EPSS 0,9%Публичный эксплойтНет опубликованного исправления
CVE-2025-51501
Reflected Cross-Site Scripting (XSS) in the id parameter of the live_edit.module_settings API endpoint in Microweber CMS2.0 allows execution of arbitrary JavaScript.
Высокий · CVSS 7.6EPSS 0,58%Нет опубликованного исправления
CVE-2025-51503
A Stored Cross-Site Scripting (XSS) vulnerability in Microweber CMS 2.0 allows attackers to inject malicious scripts into user profile fields, leading to arbitrary JavaScript execution in admin browsers.
php-jwt v6.11.0 was discovered to contain weak encryption. NOTE: this issue has been disputed on the basis that key lengths are expected to be set by an application, not by this library. This dispute is subject to review under CNA rules 4.1.4, 4.1.14, and other rules; the dispute tagging is not meant to recommend an outcome for this CVE Record.
Versions of the package z-push/z-push-dev before 2.7.6 are vulnerable to SQL Injection due to unparameterized queries in the IMAP backend. An attacker can inject malicious commands by manipulating the username field in basic authentication. This allows the attacker to access and potentially modify or delete sensitive data from a linked third-party database.
**Note:** This vulnerability affects Z-Push installations that utilize the IMAP backend and have the IMAP_FROM_SQL_QUERY option configured.
Mitigation
Change configuration to use the default or LDAP in backend/imap/config.php
php
define('IMAP_DEFAULTFROM', '');
or
php
define('IMAP_D
CodeIgniter4's ImageMagick Handler has Command Injection Vulnerability
CodeIgniter is a PHP full-stack web framework. A command injection vulnerability present in versions prior to 4.6.2 affects applications that use the ImageMagick handler for image processing (`imagick` as the image library) and either allow file uploads with user-controlled filenames and process uploaded images using the `resize()` method or use the `text()` method with user-controlled text content or options. An attacker can upload a file with a malicious filename containing shell metacharacters that get executed when the image is processed or provide malicious text content or options that get executed when adding text to images Users should
HAX CMS allows you to manage your microsite universe with PHP or NodeJs backends. In versions 11.0.13 and below of haxcms-nodejs and versions 11.0.8 and below of haxcms-php, API endpoints do not perform authorization checks when interacting with a resource. Both the JS and PHP versions of the CMS do not verify that a user has permission to interact with a resource before performing a given operation. The API endpoints within the HAX CMS application check if a user is authenticated, but don't check for authorization before performing an operation. This is fixed in versions 11.0.14 of haxcms-nodejs and 11.0.9 of haxcms-php.
HAX CMS' application pages are vulnerable to clickjacking
HAX CMS allows users to manage their microsite universe with a NodeJS or PHP backend. In haxcms-nodejs versions 11.0.12 and below and in haxcms-php versions 11.0.7 and below, all pages within the HAX CMS application do not contain headers to prevent other websites from loading the site within an iframe. This applies to both the CMS and generated sites. An unauthenticated attacker can load the standalone login page or other sensitive functionality within an iframe, performing a UI redressing attack (clickjacking). This can be used to perform social engineering attacks to attempt to coerce users into performing unintended actions within the HAX
LibreNMS has Authenticated Local File Inclusion in ajax_form.php that Allows RCE
LibreNMS is an auto-discovering PHP/MySQL/SNMP based network monitoring which includes support for a wide range of network hardware and operating systems. LibreNMS versions 25.6.0 and below contain an architectural vulnerability in the ajax_form.php endpoint that permits Remote File Inclusion based on user-controlled POST input. The application directly uses the type parameter to dynamically include .inc.php files from the trusted path includes/html/forms/, without validation or allowlisting. This pattern introduces a latent Remote Code Execution (RCE) vector if an attacker can stage a file in this include path — for example, via symlink, dev
Insecure Direct Object Reference in extension "femanager" (femanager)
The femanager extension for TYPO3 allows Insecure Direct Object Reference resulting in unauthorized modification of userdata. This issue affects femanager version 6.4.1 and below, 7.0.0 to 7.5.2 and 8.0.0 to 8.3.0
Insecure Direct Object Reference in extension "powermail" (powermail)
The powermail extension for TYPO3 allows Insecure Direct Object Reference resulting in download of arbitrary files from the webserver. This issue affects powermail version 12.0.0 up to 12.5.2 and version 13.0.0
Dolibarr has Remote Code Execution Vulnerability (Bypass)
# Summary
The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu:
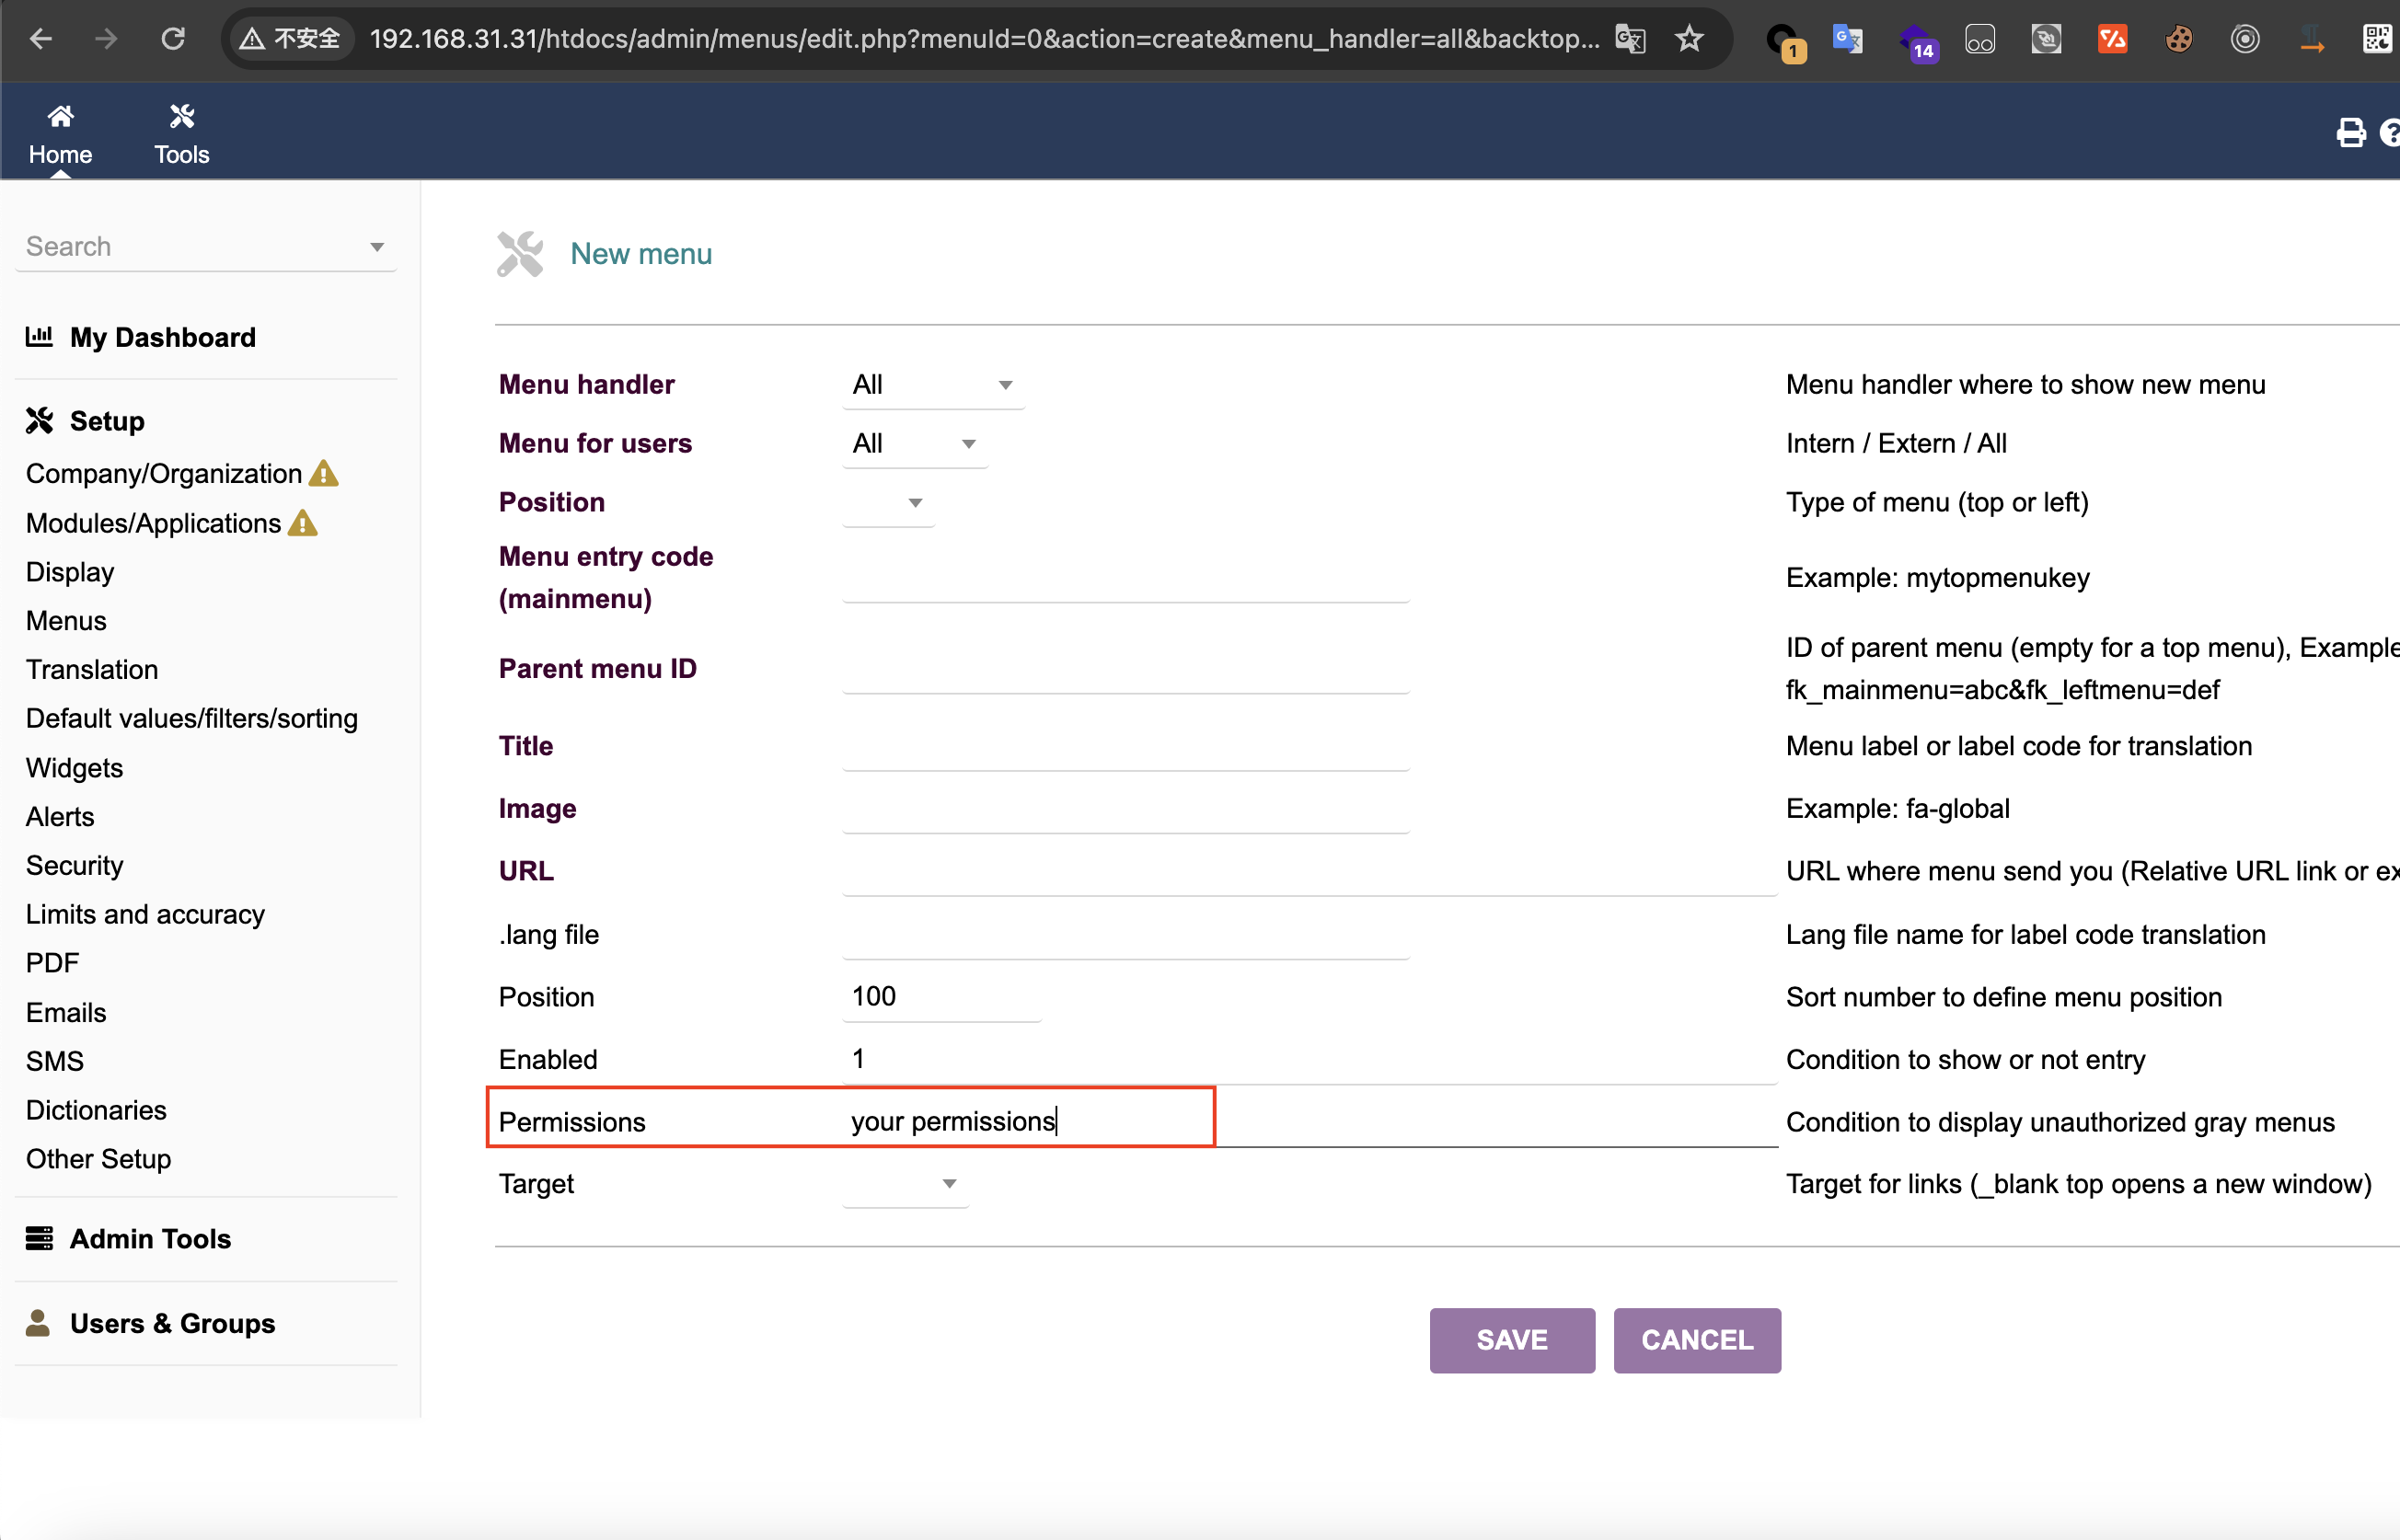
This is the trigger point of the vulnerability. The submitted permission can be php code, and it will be executed when viewing the created Menu:
- htdocs/admin/menus/edit.php
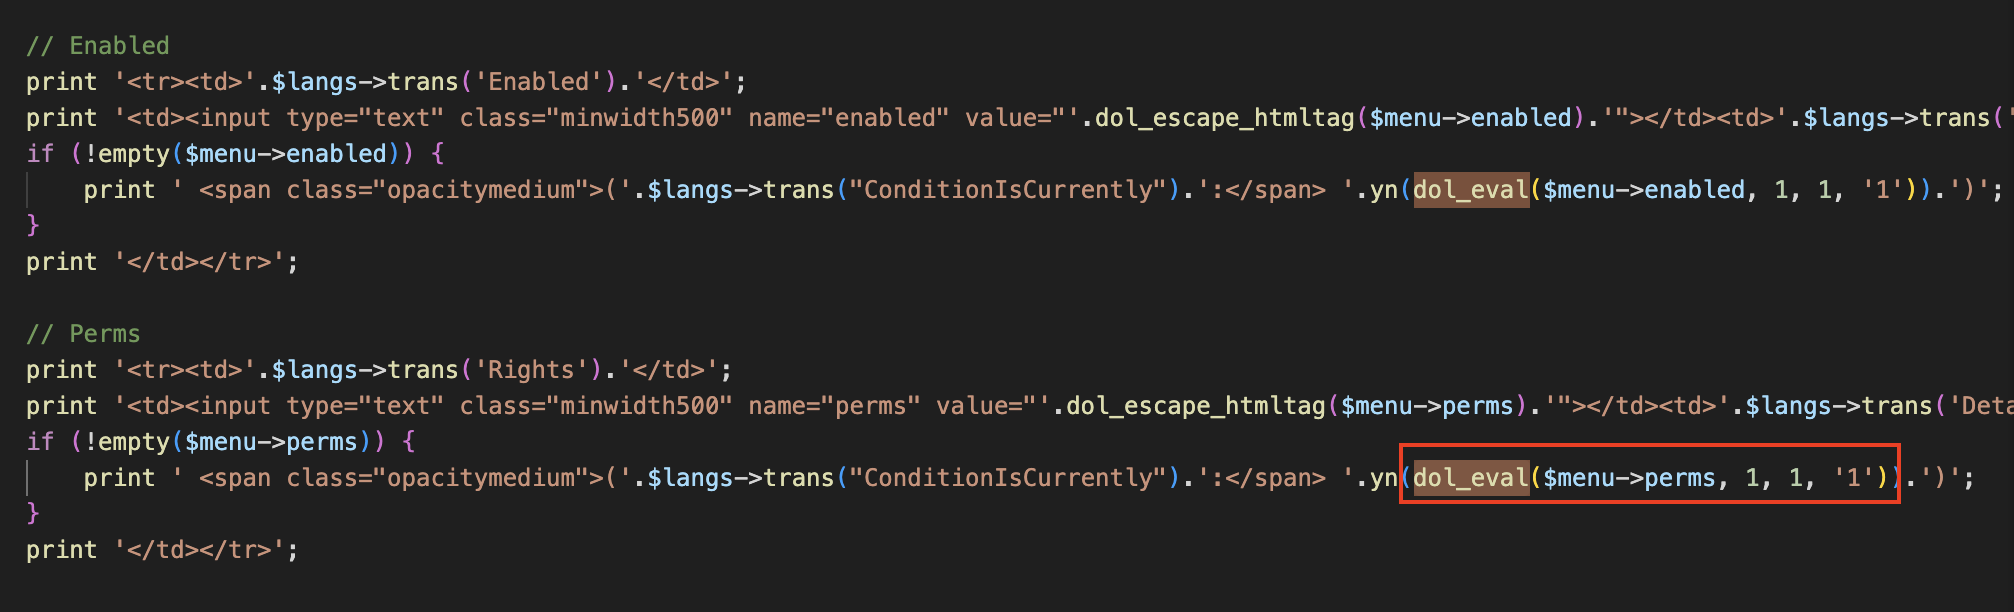
As you can see, in edit.php, if the created menu is set to `$menu->perms`, the `dol_eval()` method will be called. Following the `dol_eval()` method, we can see
Missing Authorization vulnerability in Drupal File Download allows Forceful Browsing.This issue affects File Download: from 0.0.0 before 1.9.0, from 2.0.0 before 2.0.1.
Real-time SEO for Drupal - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-091
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Real-time SEO for Drupal allows Cross-Site Scripting (XSS).This issue affects Real-time SEO for Drupal: from 2.0.0 before 2.2.0.
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Block Attributes allows Cross-Site Scripting (XSS).This issue affects Block Attributes: from 0.0.0 before 1.1.0, from 2.0.0 before 2.0.1.
Cookies Addons - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-087
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Cookies Addons allows Cross-Site Scripting (XSS).This issue affects Cookies Addons: from 1.0.0 before 1.2.4.